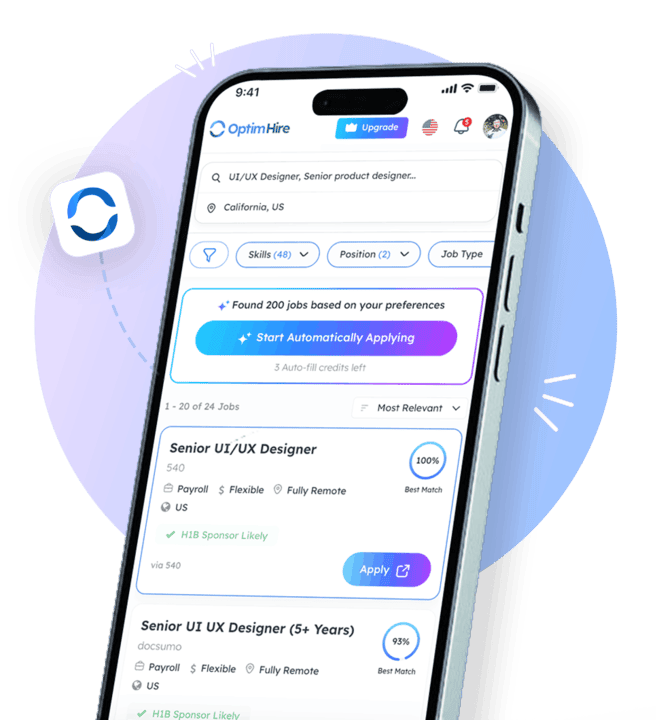
 We're excited to introduce the all new OptimHire Mobile App

OptimHire’s Job Auto-Applier that will automatically apply to jobs at 300,000+ Companies.
Critical Solutions is seeking an experienced Incident Response Analyst to support a cybersecurity operations centre (SOC) for a federal program in Ashburn, Virginia. The IR will Utilize state of the art technologies such as host forensics tools(FTK/Encase), Endpoint Detection & Response tools, log analysis (Splunk) and network forensics (full packet capture solution) to perform hunt and investigative activity to examine endpoint and network-based data.
PRIMARY ROLES AND RESPONSIBILITIES:
BASIC QUALIFICATIONS:
PREFERRED QUALIFICATIONS:
SCHEDULE
Shift schedule will be determined at the time of the start date
Clearance Requirement: Must be a US Citizen and possess an active DoD Secret Clearance. In addition, selected candidates must undergo a background investigation (BI) and fingerprinting by the federal agency and successfully pass the preceding to qualify for the position. US CITIZENSHIP IS REQUIRED.
Security Officers
Technical Support Specialists
Systems Analysts
Information Security Analyst
Operations Analyst
Technology Analyst
Malware - 3 years
Python - 1 years
IT Management - 3 years
 Get the OptimHire App
Search smarter, apply faster, and track application on the go with the OptimHire App.

AI Powered
Job Search

Access to
10M Jobs

Auto-Apply
to Job

AI Powered
Custom Resumes


 Refer & Earn